The word “ransomware” tends to conjure images of massive corporations or government agencies caught in dramatic headline-grabbing breaches, but the reality looks quite different on the ground.
Small businesses, often lacking dedicated security staff or robust backup systems, have become some of the most frequently targeted victims of ransomware attacks, facing consequences that can prove genuinely devastating for an organization without the resources of a larger company to absorb the impact.
Understanding exactly how these attacks unfold, and why smaller organizations have become such attractive targets, helps clarify why this threat deserves serious attention regardless of a business’s size.
What Ransomware Actually Does to a System
Ransomware is a category of malicious software that encrypts files on an infected computer or network, rendering them completely inaccessible until a ransom gets paid to the attacker in exchange for a decryption key. Once activated, it can spread rapidly across a connected network, locking not just a single computer but potentially every file server, shared drive, and backup system a business relies on for daily operations.
The encryption itself is typically mathematically robust, meaning victims generally can’t simply reverse it through technical means without the specific decryption key the attacker holds. This leaves affected businesses facing an agonizing choice between paying a ransom with no guarantee of recovery, or attempting to rebuild entirely from scratch without access to critical files.
The Typical Stages of a Ransomware Attack
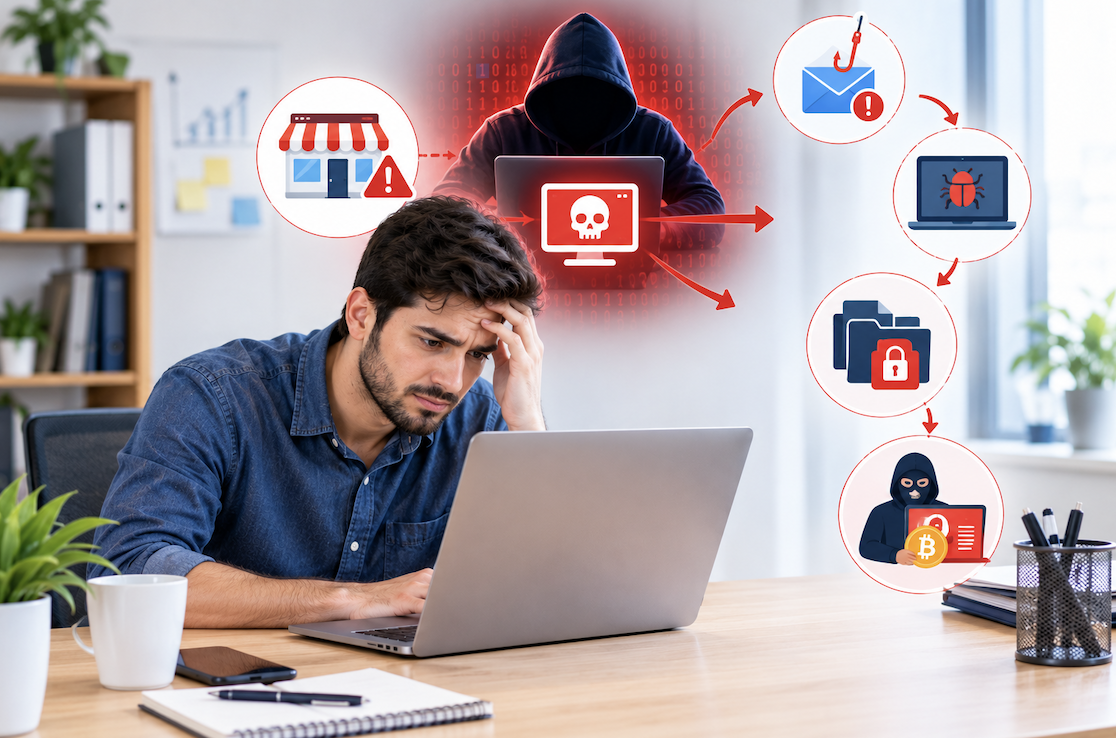
- Initial access: attackers gain entry through phishing, weak passwords, or unpatched software
- Lateral movement: the malware spreads across connected systems and networks
- Encryption: files across the network get encrypted, becoming inaccessible
- Ransom demand: attackers demand payment, typically in cryptocurrency, for decryption
Why Small Businesses Have Become Frequent Targets
Larger corporations often invest heavily in dedicated security teams, sophisticated monitoring systems, and regular security audits, making them harder, though not impossible, targets for attackers to successfully breach. Small businesses frequently lack these resources entirely, relying on outdated software, weak password practices, and minimal employee security training that leaves obvious gaps for attackers to exploit.
Attackers have also recognized that small businesses often feel more pressure to pay a ransom quickly, since prolonged downtime can threaten a smaller organization’s very survival in a way it might not for a larger company with more financial cushion to absorb an extended disruption while working through recovery options.
- Limited security budgets leave smaller organizations with fewer protective measures
- Outdated software and weak passwords create easier entry points for attackers
- Minimal security training leaves employees vulnerable to phishing attempts
- Financial pressure often makes smaller businesses more likely to pay quickly
How Attackers Typically Gain Initial Access
Phishing emails remain the most common entry point, tricking an employee into clicking a malicious link or opening an infected attachment disguised as a legitimate business communication. A single successful phishing attempt, exploiting one moment of inattention from one employee, can provide attackers with the foothold needed to begin spreading malware across an entire network.
Unpatched software vulnerabilities offer another common entry route, since attackers actively scan for systems running outdated software with known security flaws that haven’t yet been fixed through an available update. Weak or reused passwords, particularly on remote access systems, provide a third common pathway, especially when businesses haven’t implemented additional protections like two-factor authentication.
- Phishing emails tricking employees into clicking malicious links or attachments
- Unpatched software containing known, exploitable security vulnerabilities
- Weak or reused passwords, particularly on remote access and administrative accounts
- Compromised third-party vendors or software supply chains providing indirect access
The Real Financial and Operational Impact on a Small Business
Beyond the ransom demand itself, which can range from a few thousand to hundreds of thousands of dollars, businesses face substantial additional costs including lost revenue during downtime, expenses for recovery and forensic investigation, and potential legal liability if customer data was compromised during the breach.
For many small businesses, the operational disruption alone proves more damaging than the ransom itself. An inability to access critical files, process orders, or serve customers for days or weeks can permanently damage relationships and revenue in ways that persist well beyond the immediate technical recovery, sometimes contributing directly to a business closing permanently in severe cases.
- Ransom payments themselves represent only part of the total financial impact
- Lost revenue during operational downtime often exceeds the ransom demand itself
- Recovery costs, including forensic investigation, add significant additional expense
- Reputational damage and customer trust loss can persist long after technical recovery
Why Paying the Ransom Doesn’t Guarantee Recovery
Even businesses that decide to pay a ransom face genuine uncertainty about whether attackers will actually provide a working decryption key afterward, since there’s no enforceable guarantee behind a criminal transaction conducted with anonymous attackers who have no legal obligation to follow through on their end of the exchange.
Security researchers have documented numerous cases where businesses paid a ransom and either received a decryption key that didn’t fully work, or received nothing at all after payment, having lost both their money and their access to critical files simultaneously. Some attackers have also been known to demand additional payment after an initial ransom was already paid, treating the first payment as confirmation that a victim is willing and able to pay further sums.
- No guarantee exists that attackers will provide a working decryption key after payment
- Some victims receive partially functional or completely non-functional decryption tools
- Paying a ransom can mark a business as a willing target for future, repeated attacks
- Law enforcement generally advises against payment, though the decision remains complex for victims
Practical Steps That Meaningfully Reduce Risk
Regular, tested backups stored separately from a business’s main network represent perhaps the single most effective defense, since a business with reliable, isolated backups can often restore operations without needing to negotiate with attackers at all, regardless of whether files on the primary network get encrypted.
Employee training focused specifically on recognizing phishing attempts, combined with keeping software updated and enabling two-factor authentication on critical accounts, addresses the most common entry points attackers rely on. These measures don’t require a large security budget, making them genuinely accessible even for small businesses without dedicated technical staff on hand.
- Maintain regular, tested backups stored separately from the main business network
- Train employees specifically to recognize and report phishing attempts
- Keep all software updated promptly to close known security vulnerabilities
- Enable two-factor authentication on all critical business accounts and systems
A Closer Look at How One Small Business Recovered Without Paying
Consider a family-owned accounting firm that arrived one Monday morning to find every computer on their network displaying a ransom note, with client files completely inaccessible. Panic set in immediately, given how much sensitive client tax information sat locked behind the attackers’ encryption.
Because the firm had, somewhat reluctantly, invested in an automated backup system just eight months earlier after a consultant’s recommendation, their IT contractor was able to wipe the infected systems entirely and restore from a backup taken the previous night. They lost less than a full day of new data entry and never considered paying the ransom at all. The owner later admitted the backup investment had felt like an unnecessary expense at the time, a sentiment that vanished entirely once it turned out to be the single decision that saved the business from what could have been a genuinely existential crisis.
The Growing Role of Cybersecurity Insurance in Recovery Planning
As ransomware attacks have become more common, cyber insurance has emerged as an increasingly important tool for small businesses seeking to limit financial exposure from a successful attack. Policies vary considerably in what they cover, with some including costs for forensic investigation, legal liability,
and even ransom negotiation support, while others offer more limited protection focused narrowly on data recovery expenses alone.
Insurers have also begun requiring policyholders to meet specific baseline security standards, such as maintaining backups and enabling multi-factor authentication, before extending coverage at all. This shift has had the secondary effect of pushing many small businesses toward adopting better security practices simply to qualify for affordable coverage, turning insurance requirements into an unexpected driver of genuine security improvement.
- Cyber insurance policies vary widely in scope and covered expenses
- Insurers increasingly require baseline security measures before offering coverage
- Meeting these requirements often improves overall security posture as a side benefit
- Comparing policies carefully helps businesses find coverage matching their actual risk
Building a Response Plan Before an Attack Happens
Businesses that have thought through a response plan in advance, including who to contact, how to isolate affected systems quickly, and whether cyber insurance coverage exists, tend to recover considerably faster than those scrambling to figure out basic response steps for the first time during an actual, active attack.
Consulting with a cybersecurity professional, even briefly, to assess specific vulnerabilities and establish basic protective measures represents a worthwhile investment for most small businesses, given the potentially severe consequences an unprepared organization faces if targeted by a genuinely determined attacker.
- Establish a clear response plan before an attack occurs, not during one
- Identify who to contact immediately, including IT support and potentially law enforcement
- Consider cyber insurance coverage appropriate to a business’s specific risk level
- Periodically review and update the response plan as the business and threats evolve
Final Thoughts
Ransomware has evolved into a genuine, persistent threat facing organizations of every size, with small businesses often bearing a disproportionate share of the risk due to limited security resources and heightened pressure to resolve an attack quickly. Understanding how these attacks unfold, and investing in practical, accessible defenses, offers small businesses a realistic path toward meaningfully reducing this risk without requiring an enterprise-level security budget.
Frequently Asked Questions
1. Should a small business ever consider paying a ransomware demand?
Most law enforcement agencies advise against payment, given the uncertainty of recovery and risk of future targeting, though the decision remains genuinely difficult for affected businesses facing severe operational disruption.
2. How often should a small business back up its critical data?
This depends on how frequently data changes, though daily backups are common for actively used business data, with backups stored separately from the main network for genuine protection.
3. Can antivirus software alone prevent a ransomware attack?
Antivirus software helps but isn’t sufficient alone, since attacks often exploit human error through phishing, making employee training an equally important layer of defense.
4. Is cyber insurance worth the cost for a small business?
For many small businesses, yes, given the potentially severe financial impact of an attack, though coverage details and costs vary considerably and deserve careful comparison.
5. How quickly can a well-prepared business recover from a ransomware attack?
Businesses with reliable, tested backups and a clear response plan can often restore operations within days, compared to weeks or longer for unprepared organizations facing the same attack.
6. Do ransomware attackers specifically target certain industries more than others?
Healthcare, legal, and financial services are frequently targeted due to sensitive data and urgency around restoring access, though attackers generally target any organization with exploitable weaknesses.
7. Can cloud-based file storage alone replace the need for separate backups?
Not entirely, since some cloud storage syncs changes in real time, meaning encrypted files could overwrite clean ones unless separate, version-controlled backups are also maintained.